Domains
Configure Citadel origins and hostnames
Configure the backend Citadel forwards clean traffic to: apex host, port and TLS-to-origin, plus protected subdomains that share or override it.
Configure the backend
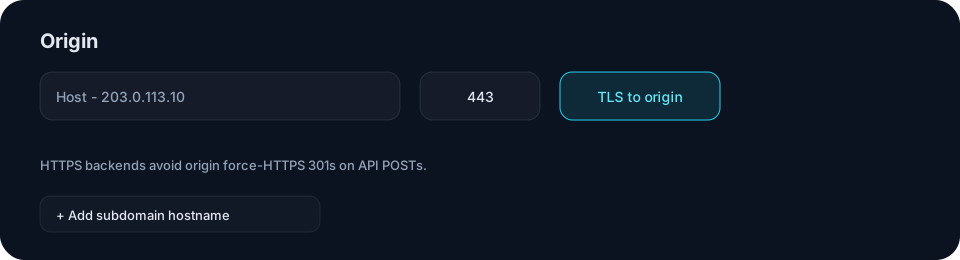
The origin is the real server Citadel sends clean traffic to. Set the apex host, port and TLS-to-origin option, then add protected subdomains. A subdomain can share the apex backend or override it.
- Confirm the apex origin URL reaches a working server.
- Add every hostname you want Citadel to protect.
- Give each hostname a proxied Cloudflare DNS record pointing at the Citadel ingress IP.
- Save, then use Origin health to test the connection.
API and SSO redirects
If the origin redirects HTTP to HTTPS, enable TLS-to-origin or use an HTTPS backend. This helps prevent POST requests to /api/* from being turned into 301 redirects.