Configure Citadel allowlists
Bypass challenges for trusted paths, IPs, and user agents on every hostname.
Add a bypass
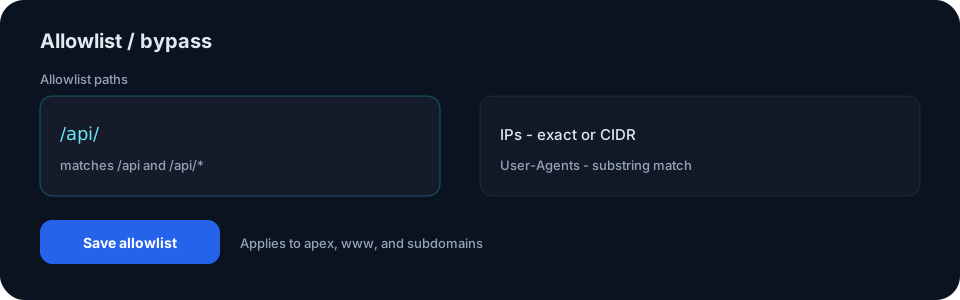
Open Security → Allowlist / bypass, add specific rules, then Save allowlist. Matching clients bypass challenges, including Lockdown, across the apex, www, and protected subdomains for that domain.
Path rules
Paths must start with /. /api/ matches /api, /api/, and descendants such as /api/auth/google. /api also matches descendants but not /apiv2. Keep rules specific because other security features can still depend on rule order.
IP and User-Agent rules
Enter an exact IPv4/IPv6 address or CIDR, such as 203.0.113.0/24. Behind trusted Cloudflare edges, Citadel uses the visitor or webhook source IP from CF-Connecting-IP or X-Real-IP; do not allowlist Cloudflare's shared IPs. User-Agent uses a substring match, such as Stripe/ or UptimeRobot, and is easier to spoof than path or IP matching.